Account Contatti
Il tuo carrello
Spedizione DPD & FedEx
Serve aiuto? Chiedi all'AI

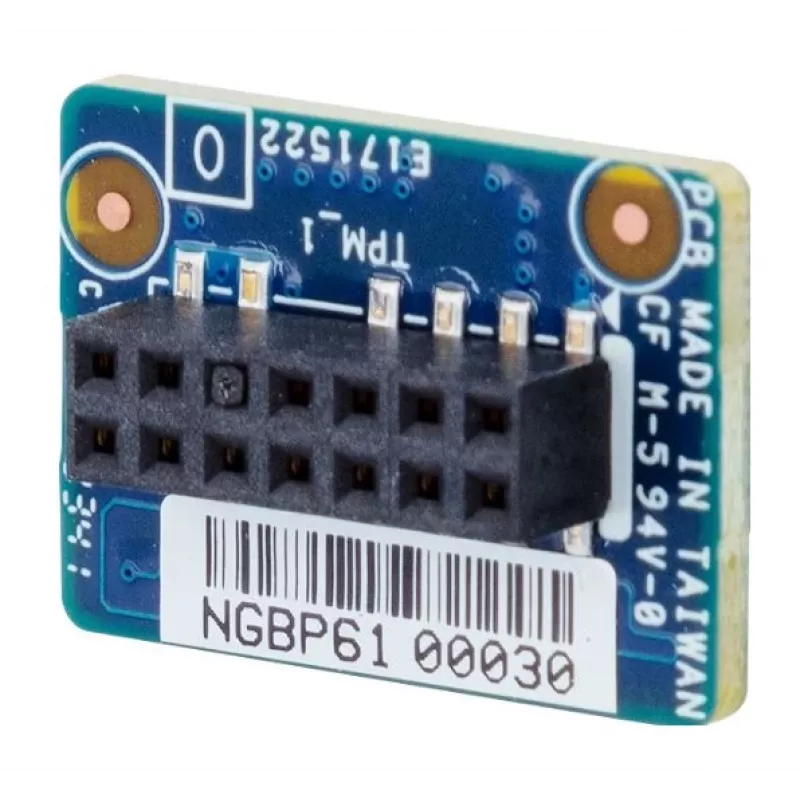
Scheda modulo TPM GIGABYTE CTM012 2.0 — Trusted Platform Module per la sicurezza della scheda madre

Scheda modulo TPM GIGABYTE CTM012 2.0 — Trusted Platform Module per la sicurezza della scheda madre
40,00 €
GIGABYTE TPM Module Card CTM012 2.0 is a Trusted Platform Module designed to provide hardware-based security functions for compatible motherboards. The module offers secure storage for cryptographic keys, supports platform integrity verification and BIOS/boot protection, and enables operating system... Leggi di più
Stock 1 Codice 2525021 Marca GIGABYTE Modello 9CTM012NR-00 Garanzia 2 anni

Spedizioni e resi

Consegna stimata Venerdì, Ottobre 23
Ti terremo aggiornato tramite il nostro sistema di tracciamento dettagliato
Opzioni di pagamento
Carta di credito/debitoVisaMastercardPayPalApple PayGoogle PayBonifico bancario

GIGABYTE TPM Module Card CTM012 2.0 is a Trusted Platform Module designed to provide hardware-based security functions for compatible motherboards. The module offers secure storage for cryptographic keys, supports platform integrity verification and BIOS/boot protection, and enables operating system features and applications that require TPM. It is a compact add-on card that integrates with supported GIGABYTE motherboards to extend system security capabilities without changing existing software.

Advantages

The TPM module delivers a hardware root of trust for cryptographic operations and key storage, reducing reliance on software-only protections. It supports secure boot and platform attestation to help verify system integrity during startup. The module is designed for straightforward integration with compatible motherboards, occupying minimal board space while offering persistent, tamper-resistant storage for encryption keys and certificates. Its presence enables native OS security features and enterprise management workflows that depend on TPM functionality.

Suitable for

  • Enabling operating system features that require TPM (disk encryption, credential protection)
  • Secure boot and BIOS/firmware integrity verification
  • Hardware-backed key storage for encryption and authentication
  • Enterprise and workstation systems that need platform attestation and enhanced security

Key specifications

  • TPM version: 2.0 compliant specification
  • Form factor: compact module card for compatible motherboard TPM header
  • Functionality: secure cryptographic key storage, platform integrity verification, secure boot support
  • Compatibility: designed for use with compatible GIGABYTE motherboards supporting external TPM modules
  • Data persistence: tamper-resistant non-volatile storage for keys and credentials

How to use

Install the TPM module into the dedicated TPM header on a compatible motherboard following the motherboard manufacturer’s instructions. After physical installation, enable TPM support in the motherboard BIOS/UEFI and update firmware if required. Once the system recognizes the module, enable the desired operating system security features such as disk encryption (BitLocker or equivalent), secure boot, or credential protection. Manage TPM keys and policies using the OS or enterprise management tools according to your security requirements.

Recommendations

Confirm motherboard compatibility and BIOS/UEFI support before installation. Back up critical data and record TPM ownership/recovery keys when enabling encryption features. Keep motherboard firmware up to date and follow vendor guidance for secure configuration and key management.

Punti salienti
  • Enabling operating system features that require TPM (disk encryption, credential protection)
  • Secure boot and BIOS/firmware integrity verification
  • Hardware-backed key storage for encryption and authentication
  • Enterprise and workstation systems that need platform attestation and enhanced security
  • TPM version: 2.0 compliant specification
  • Form factor: compact module card for compatible motherboard TPM header
  • Functionality: secure cryptographic key storage, platform integrity verification, secure boot support
  • Compatibility: designed for use with compatible GIGABYTE motherboards supporting external TPM modules
  • Data persistence: tamper-resistant non-volatile storage for keys and credentials
Storico prezzi degli ultimi 6 mesi
Scheda modulo TPM GIGABYTE CTM012 2.0 — Trusted Platform Module per la sicurezza della scheda madre
Attuale
40,00 €
Minimo
39,30 €
Massimo
82,40 €
Variazione 24 h
+0,61 €   +2%
Settimana
+0,69 €   +2%
Mese
-41,65 €   -51%
Ciao, sono l'assistente AI di DistriNode. Posso aiutarti a trovare prodotti, confrontare le opzioni, creare preventivi in PDF o aprire richieste di assistenza.